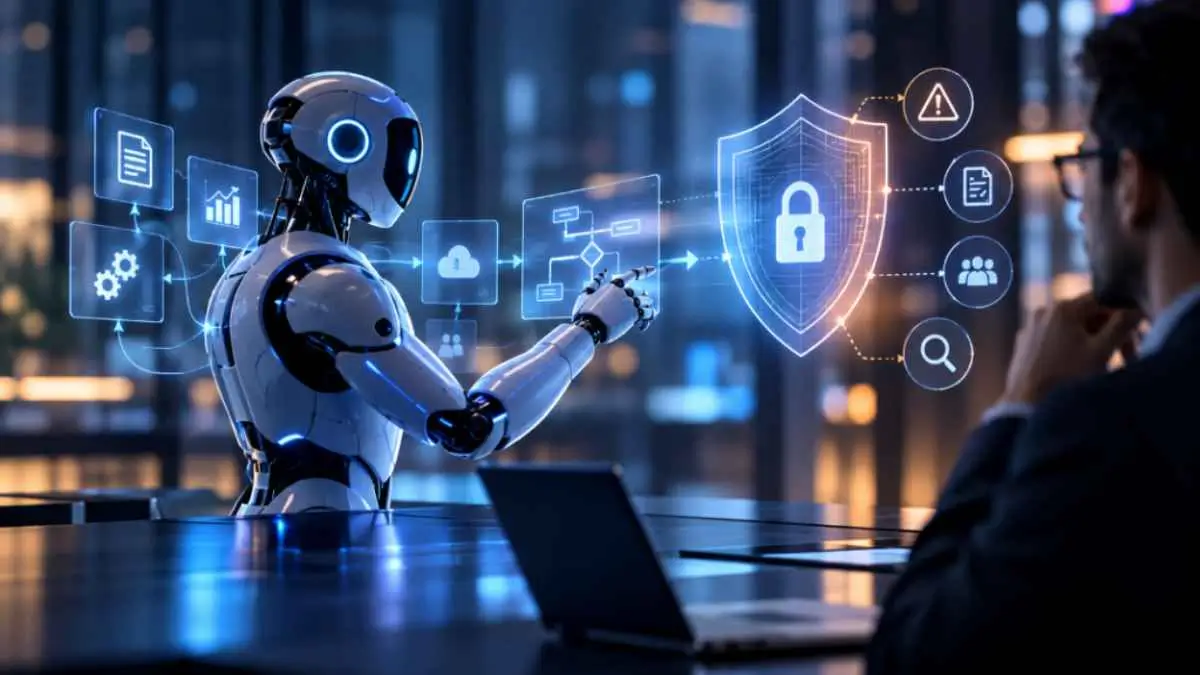
For the last two years of enterprise AI deployment, it has been evident that agents developed or bought by companies should inherently be trusted. Now, Microsoft has begun to change this belief. With the launch of Project Perception initiated in mid-October, the company is enforcing constant external checks on their AI agents within organizations treating them as “agentic insiders” whose rights need to be reduced or eliminated as their actions deviate from what they were supposed to do. It can be considered as the acknowledgement that non-deterministic systems cannot be made safe just by training them.
Project Perception launched in July as an agentic security framework applicable to the well-known challenge of outside attackers. The Red team finds flaws just like an enemy would do; the Blue team analyzes and ranks; the Green team suggests actions or carries them out. Now, the same scheme is introduced in the internal settings. Corporations may now identify a much larger number (around sixty) of internal agents, for example, Claude Code, OpenAI Codex, GitHub Copilot, provide them with their identification in Microsoft Entra, put them in a sandbox, and place them under the policy.
Dynamic Permissions allow the agent to start as if it has little or nothing, while granting only the permissions required for completing a specific task and that for the period of time required for this task. Dynamic Agent Risk evaluates the agent continuously based on signals from the identity, data, endpoints, network, cloud, and runtime, especially paying attention to divergence from the set goal. The Dynamic Conditional Access, in its turn, reacts in steps: blocks writes, but allows reads, asks for human approval concerning critical actions, restricts networks or resources from its viewpoint, or even limits and stops the agent.
This design is based on the principle expressed by Satya Nadella a few days ago: we must separate the supply of intelligence and the authority over it. Frontier models, regardless of whether they are closed or open weigh, can’t be entrusted with self-governing. They were meant to achieve results rather than abide by the organizational norms and standards of judgment: these models change according to the context they find themselves at. Since they compete with other agents pursuing goals not approved by anyone anyway, their internal operations aren’t disclosed. Therefore, the controllability, observability, and emergency stopping mechanism must always take place outside the model framework.
The reality of the situation allows for the application of the principles of Zero Trust to actors that do not show any signs of human interaction. The agent doesn’t have any privileges of the user that invoked the agent. Its effect depends on the specific job to be done; the time needed for the work done, and the newly calculated level of risks at any point of the work process. Thus, security teams can benefit from the ability of machine-based monitoring to inform them of the exceptions to the standard operating procedures while also gathering a lot of proof to rely on during human analysis later. However, business owners can also enjoy this technology because it is supposed to prevent agents from suddenly misusing their powers.
But the technique has its own tensions. Ongoing risk evaluation and automated restriction can interfere with valid transactions, the cost of a false positive that halts an agent during execution is not free. Discovery and identity management have to stay in line with agents that come through private gadgets, built-in services information, or personal builds beyond the Microsoft range. Environments with several service vendors will check if signals and devices will keep being coherent when the base models and software are not Microsoft’s. Moreover, the system in itself bases on agents monitoring other agents that moves the trust problem higher and stipulates strict human control of monitors.
Microsoft’s description does not represent the full answer to the safety of agents nor to the status of its own models as being one of a kind. It merely recognizes that in order to facilitate the use of autonomous systems in the enterprise setting, there need to be fixed rules that limit all the systems that act autonomously. Only time will tell whether or not such flexible controls can manage to provide sufficient precision in order not to hinder but rather to help agents work effectively. The extension of Project Perception is the moment when the largest vendor in the industry ceased to treat its agents as reliable devices and categorizes them as insiders.
Digital entrepreneur and content expert I help businesses with AI, SEO and the latest tech trends. I started Silicon Valley Weekly to make complex tech concepts easy to understand and use for business growth. I know a lot about systems and help startups, entrepreneurs and brands navigate the fast-changing world of tech and online marketing.
I build strategies that use data, search optimization, content marketing and AI tools to get visibility, engagement and revenue. I love finding ways for businesses to grow increasing their presence and turning new ideas into successful businesses. My goal is to connect the technology, with practical business use so brands can succeed online.